
Government Contractors
Win federal contracts with automated compliance
Defense contractors face mandatory CMMC certification, complex NIST 800-171 requirements, and rigorous FedRAMP authorization processes. Evidr automates evidence collection, SPRS scoring, and SSP generation so you can focus on winning contracts.
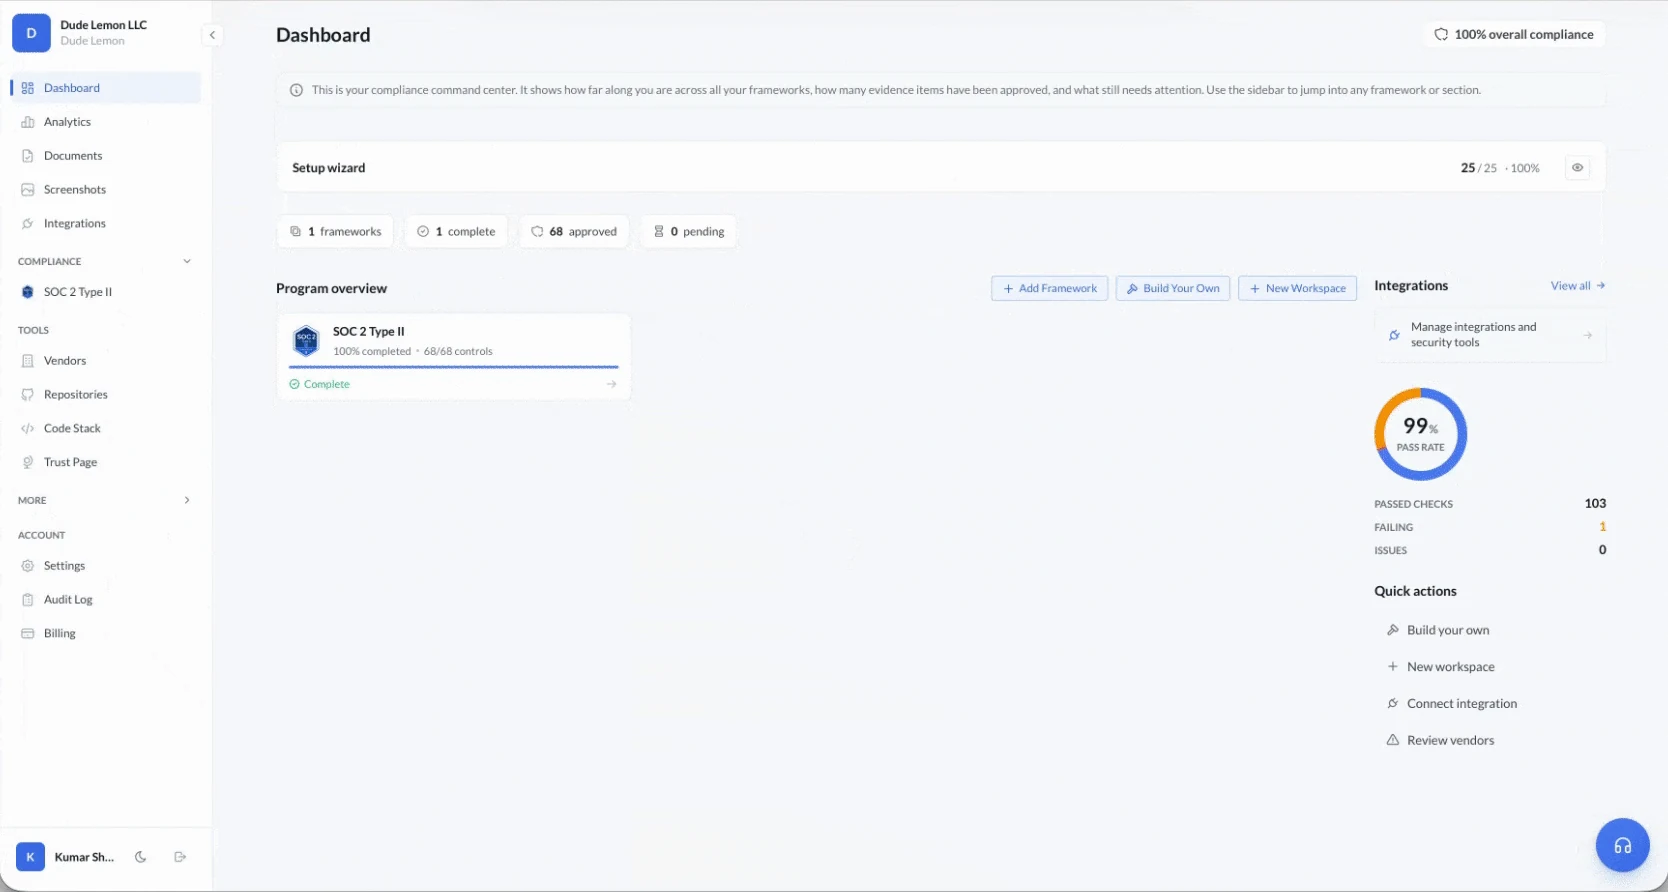
Inside the product
The whole programme on one screen.
01Why Evidr
What you get.
- 01
FedRAMP Ready
Prepare for FedRAMP authorization with automated control documentation and continuous monitoring.
- 02
CMMC Certified
Achieve CMMC Level 2 certification with NIST 800-171 mapping and C3PAO assessment preparation.
- 03
NIST Compliant
Full NIST 800-171 and 800-53 control mapping with automated evidence collection.
- 04
SPRS Scoring
Calculate and maintain your SPRS score with real-time gap analysis and remediation tracking.
02The difference
What changes.
Without automation
- CMMC certification blocks DoD contract eligibility
- 110 NIST 800-171 controls require extensive documentation
- SPRS score calculation is complex and error-prone
- FedRAMP authorization takes 12-18 months
- CUI protection requirements are stringent
- StateRAMP requires state-by-state compliance tracking
With Evidr
- Automated NIST 800-171 compliance gets you certified faster
- AI maps controls and generates System Security Plans
- Real-time SPRS scoring with gap remediation guidance
- Accelerate authorization with pre-built control baselines
- Automated CUI handling documentation and access tracking
- Unified multi-state compliance dashboard
03Government Contractors
CMMC levels
- Level 117 practices · Self-Assessment
Foundational
Basic safeguarding of FCI with annual self-assessment
- Level 2110 practices · Third-Party (C3PAO)
Advanced
Full NIST 800-171 implementation for CUI protection
- Level 3110+ practices · Government-Led
Expert
Enhanced protection against APTs with NIST 800-172
04Step by step
How it works.
- 01
Contract Analysis
Our AI analyzes your DFARS clauses and contract requirements to determine your required CMMC level and applicable controls.
- 02
Gap Assessment
Evidr maps your current security posture against NIST 800-171 and calculates your SPRS score with specific remediation recommendations.
- 03
Evidence Collection
Connect your infrastructure and automatically collect evidence for all 110 NIST 800-171 controls. AI reviews and maps each artifact.
- 04
Assessment Ready
Generate your SSP and POA&M documentation, then invite your C3PAO assessor to the secure auditor portal.
05Frameworks
The frameworks your buyers ask for.
- FedRAMPFederal cloud authorization with Low, Moderate, and High impact baselinesRead the guide
- CMMCCybersecurity Maturity Model Certification for defense contractorsRead the guide
- StateRAMPState and local government cloud security authorizationRead the guide
- NIST 800-171CUI protection requirements for non-federal systemsRead the guide
Platform
What you will use most.
Ready to get audit-ready?
Start on the free Starter plan, or talk to us about SOC 2, ISO 27001, HIPAA or any framework and see the platform on your own stack.