
ISO 27001 Certification
Achieve ISO 27001 certification in months, not years
Evidr streamlines your ISMS implementation with AI-powered risk assessment, automated control mapping, and continuous compliance monitoring. Get internationally recognized security certification faster.
Inside the product
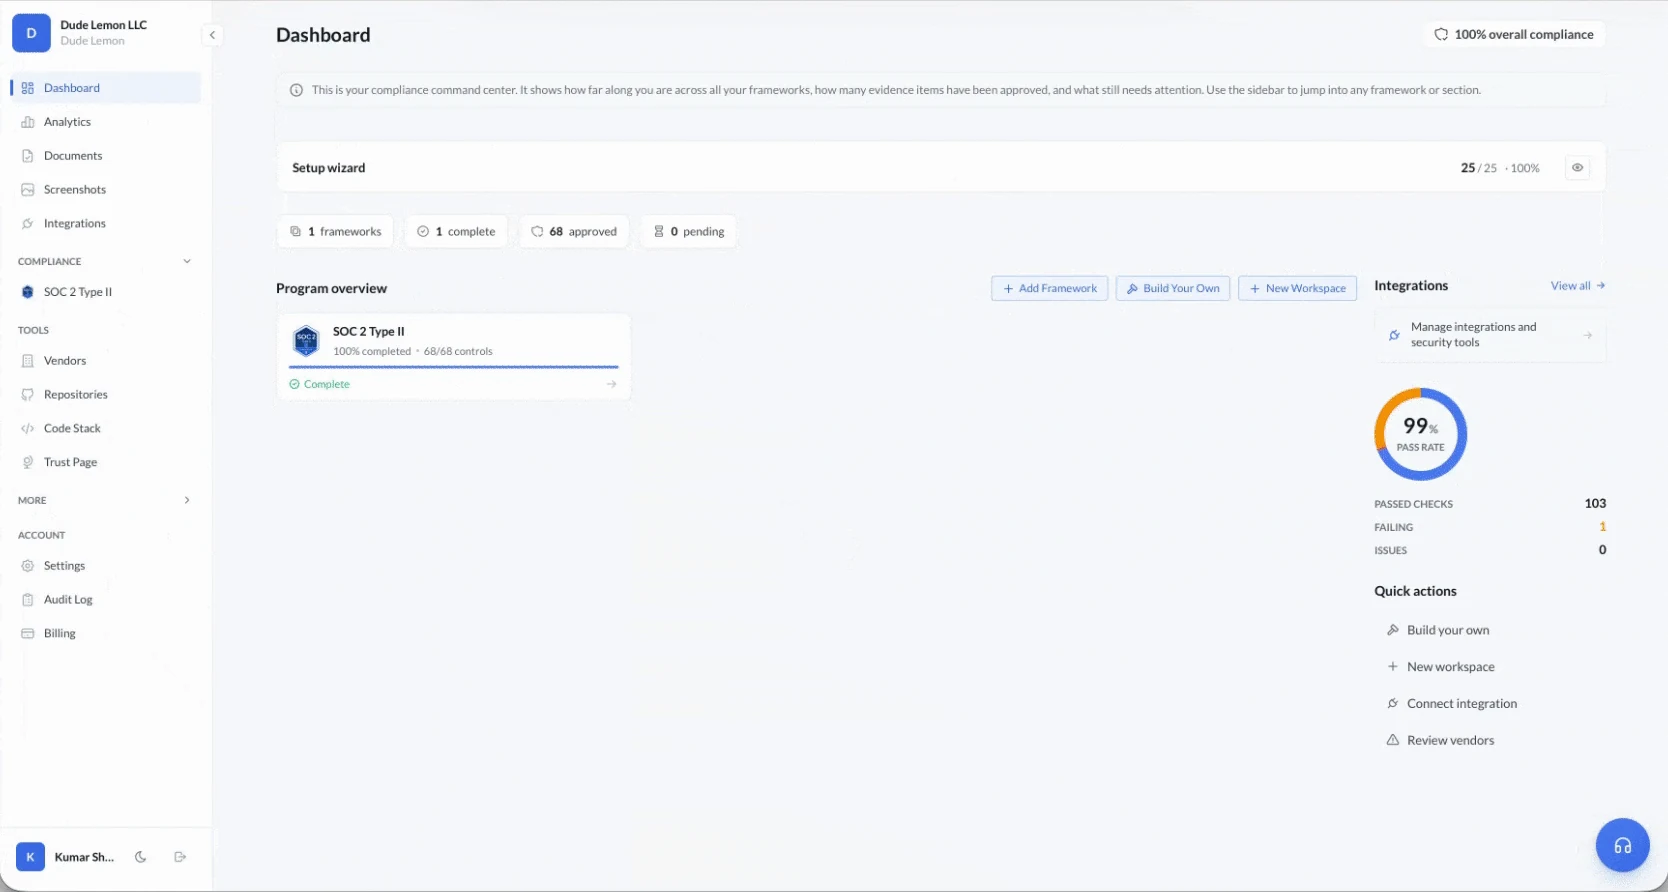
ISO 27001 in the console, control by control.
01ISO 27001
Annex A, four themes
The 93 controls of the 2022 revision, grouped the way the standard groups them.
- 0137 controls
Organizational Controls
Policies, roles, asset management, supplier security, and business continuity.
- 028 controls
People Controls
Screening, awareness, training, disciplinary processes, and remote working.
- 0314 controls
Physical Controls
Physical security perimeters, entry controls, equipment security, and clear desk.
- 0434 controls
Technological Controls
Access control, cryptography, network security, secure development, and logging.
02What Evidr does
Everything ISO 27001 asks for, handled.
- 01
AI-Powered Risk Assessment
Comprehensive risk identification and treatment planning. AI analyzes your organization profile to surface relevant threats and recommend appropriate controls.
- 02
Annex A Control Mapping
Automatic mapping of your existing controls to ISO 27001:2022 Annex A. See coverage across all 93 controls organized into 4 themes.
- 03
ISMS Policy Generation
Generate required ISMS policies in seconds. Information Security Policy, Access Control Policy, Incident Response, and 20+ templates tailored to your organization.
- 04
Continuous Compliance Monitoring
Track control effectiveness and evidence freshness. Proactive alerts before surveillance audits ensure you maintain certification year-round.
- 05
Internal Audit Management
Plan and execute internal audits with guided workflows. Document findings, corrective actions, and track remediation through the audit portal.
- 06
Statement of Applicability
Auto-generate your Statement of Applicability with justifications for included and excluded controls. Export audit-ready documentation.
03The path
ISO 27001 readiness, step by step.
- 01Week 1
Context & Scope Definition
Define ISMS scope, identify interested parties, and document organizational context. AI guides you through ISO 27001 Clause 4 requirements.
- 02Week 2-4
Risk Assessment & Treatment
Identify information assets, assess threats and vulnerabilities, and develop risk treatment plans with appropriate controls.
- 03Week 4-8
Control Implementation
Implement selected Annex A controls. Generate policies, configure technical controls, and document procedures.
- 04Week 8-10
Internal Audit & Review
Conduct internal audit, perform management review, and address any nonconformities before certification audit.
- 05Week 10-12
Certification Audit
Stage 1 documentation review, then Stage 2 implementation audit. Certification body verifies ISMS effectiveness.
04Questions
ISO 27001, answered.
Related
Often paired with ISO 27001.
Ready for ISO 27001?
Start on the free Starter plan, or talk to us and see ISO 27001 set up on your own stack.