
SOC 2 Compliance
Achieve SOC 2 audit readiness in weeks, not months
Evidr automates evidence collection, control mapping, and continuous monitoring for SOC 2 Type I and Type II. Get enterprise customers faster with AI-powered compliance automation.
Inside the product
SOC 2 in the console, control by control.
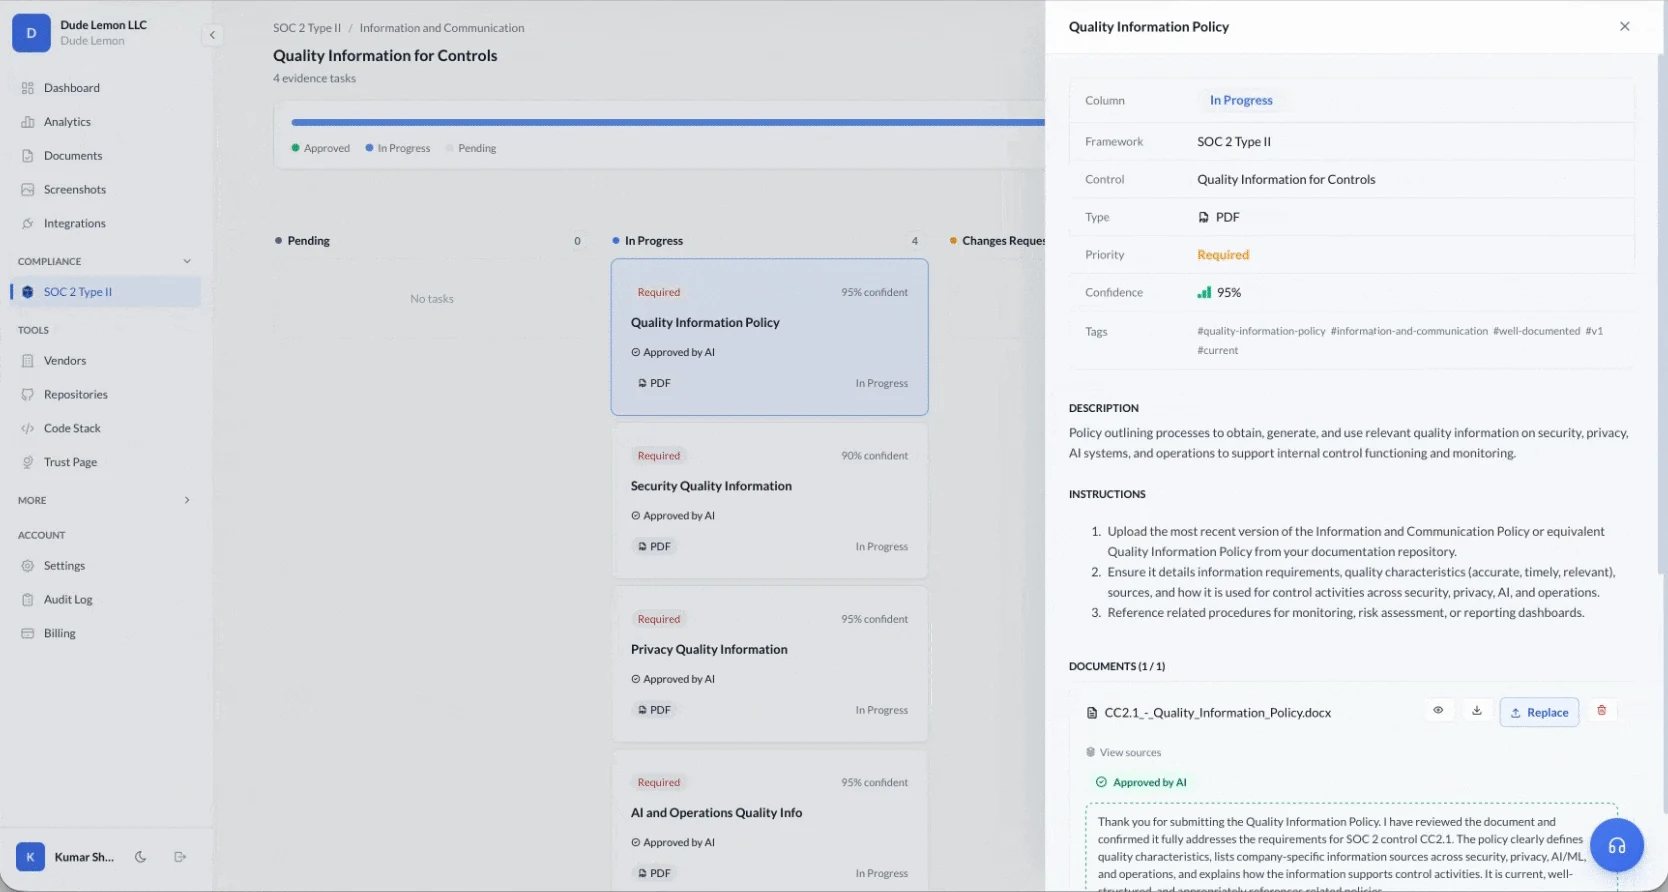
01SOC 2
Trust Service Criteria
Five criteria. Security is always in scope; the other four follow your service and your customers.
- 01Required
Security
Protection against unauthorized access. The foundation of every SOC 2 report.
- 02Optional
Availability
Systems are operational and accessible as committed in service agreements.
- 03Optional
Processing Integrity
System processing is complete, valid, accurate, timely, and authorized.
- 04Optional
Confidentiality
Information designated as confidential is protected as committed.
- 05Optional
Privacy
Personal information is collected, used, retained, and disclosed in conformity with commitments.
02What Evidr does
Everything SOC 2 asks for, handled.
- 01
Automated Control Mapping
Evidr automatically maps your infrastructure to SOC 2 Trust Service Criteria. See exactly which controls are covered and where gaps exist.
- 02
AI-Powered Evidence Collection
Upload evidence once and let AI review it with confidence scoring. Automatic classification, tagging, and control mapping on every document.
- 03
Continuous Compliance Monitoring
Track evidence expiry dates, get proactive alerts before documents go stale, and maintain audit readiness 365 days a year.
- 04
SOC 2 Policy Generation
Generate audit-ready security policies in seconds. Access Control, Incident Response, Change Management, and more, all tailored to your organization.
- 05
Auditor Portal Access
Invite your auditor to a read-only portal. They see approved evidence and controls without access to drafts or internal data.
- 06
AI Compliance Assistant
Ask questions about SOC 2 requirements, get guidance on evidence collection, and receive personalized recommendations based on your company profile.
03The path
SOC 2 readiness, step by step.
- 01Day 1
Onboarding & Scoping
AI-guided setup profiles your organization across 60+ risk signals. Frameworks and controls are generated automatically.
- 02Week 1-2
Gap Analysis & Remediation
See exactly where you stand. Evidr identifies missing controls and evidence, then guides you through remediation.
- 03Week 2-3
Evidence Collection
Upload policies, screenshots, and integrations evidence. AI reviews everything with confidence scoring.
- 04Week 3-4
Audit Readiness Review
Internal review of all controls and evidence. Address any flagged items before engaging your auditor.
- 05Week 4+
Auditor Engagement
Invite your auditor to the read-only portal. They access approved evidence directly, no back-and-forth.
04Questions
SOC 2, answered.
Related
Often paired with SOC 2.
Ready for SOC 2?
Start on the free Starter plan, or talk to us and see SOC 2 set up on your own stack.