
Product · Policy Generation
AI-generated security policies ready for board review
Stop writing policies from scratch. Evidr generates complete, framework-aligned security policies using AI, tailored to your company profile, industry, and compliance requirements. From first draft to board-ready PDF in minutes.
Inside the product
Approved by AI, with a confidence score.
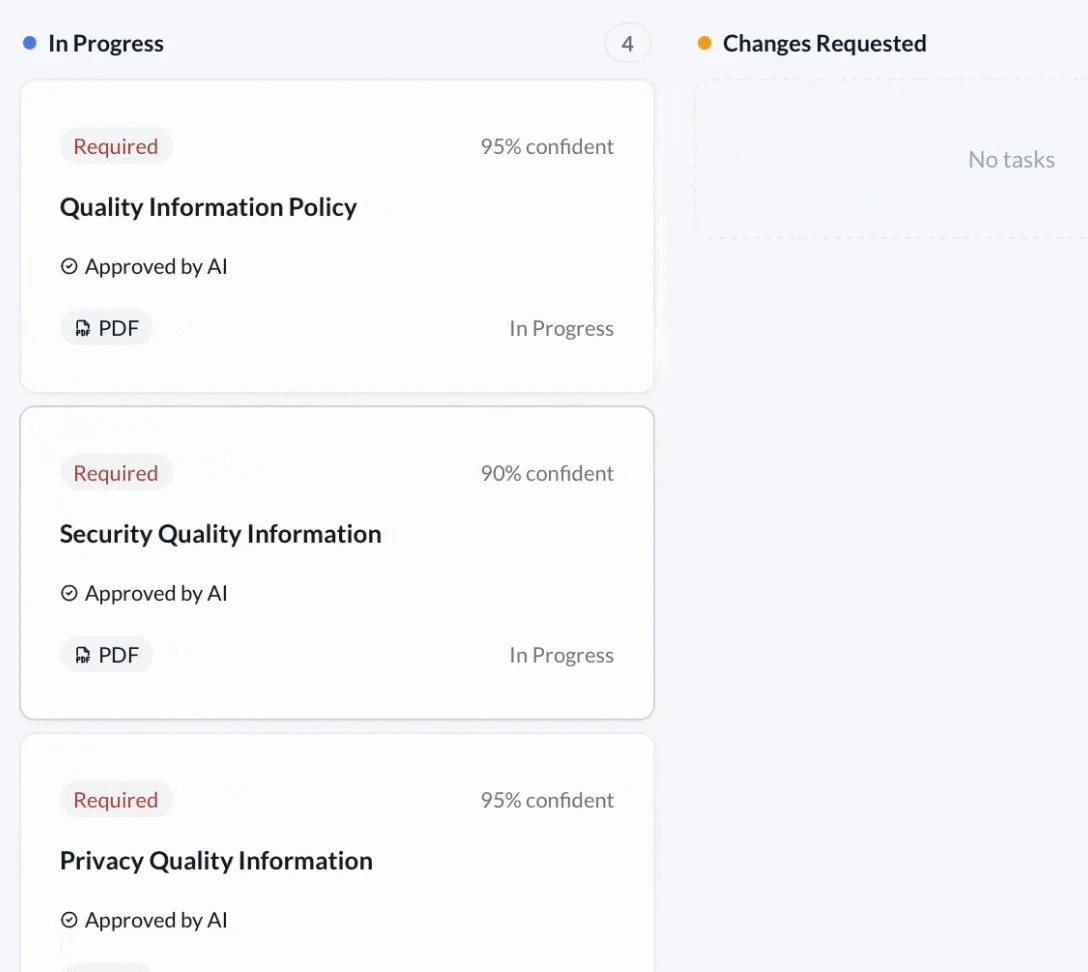
01What it does
What you get.
- 01
AI-Generated Policies
Fully written security policies tailored to your frameworks and company profile.
- 02
One-Click PDF Export
Download board-ready documents instantly for review and distribution.
- 03
Approval Workflows
Built-in review process before policies go live to your compliance workspace.
- 04
Version Control
Track every change with complete history and easy rollback.
02Step by step
How it works.
- 01
Select Framework
Choose your compliance frameworks. Evidr recommends required policies based on SOC 2, ISO 27001, HIPAA, GDPR, and more.
- 02
Generate with AI
Our AI generates complete policy documents using your company profile, industry context, and framework requirements.
- 03
Review & Approve
Edit, refine, and approve policies through the built-in workflow. Export as PDF or send for employee signatures.
03Policy Generation
Policies Evidr writes
Each one drafted for your company, your stack and your frameworks.
- Information Security Policy
- Acceptable Use Policy
- Access Control Policy
- Data Classification Policy
- Incident Response Plan
- Business Continuity Plan
- Vendor Management Policy
- Change Management Policy
- Password Policy
- Remote Work Policy
- Data Retention Policy
- Encryption Policy
Related
Works with.
Ready to get audit-ready?
Start on the free Starter plan, or talk to us about SOC 2, ISO 27001, HIPAA or any framework and see the platform on your own stack.