
GDPR Compliance
Protect EU personal data and demonstrate GDPR compliance
Evidr automates data mapping, consent tracking, DPIA workflows, and breach notification. Demonstrate accountability and avoid fines up to 4% of global revenue with AI-powered privacy compliance.
Inside the product
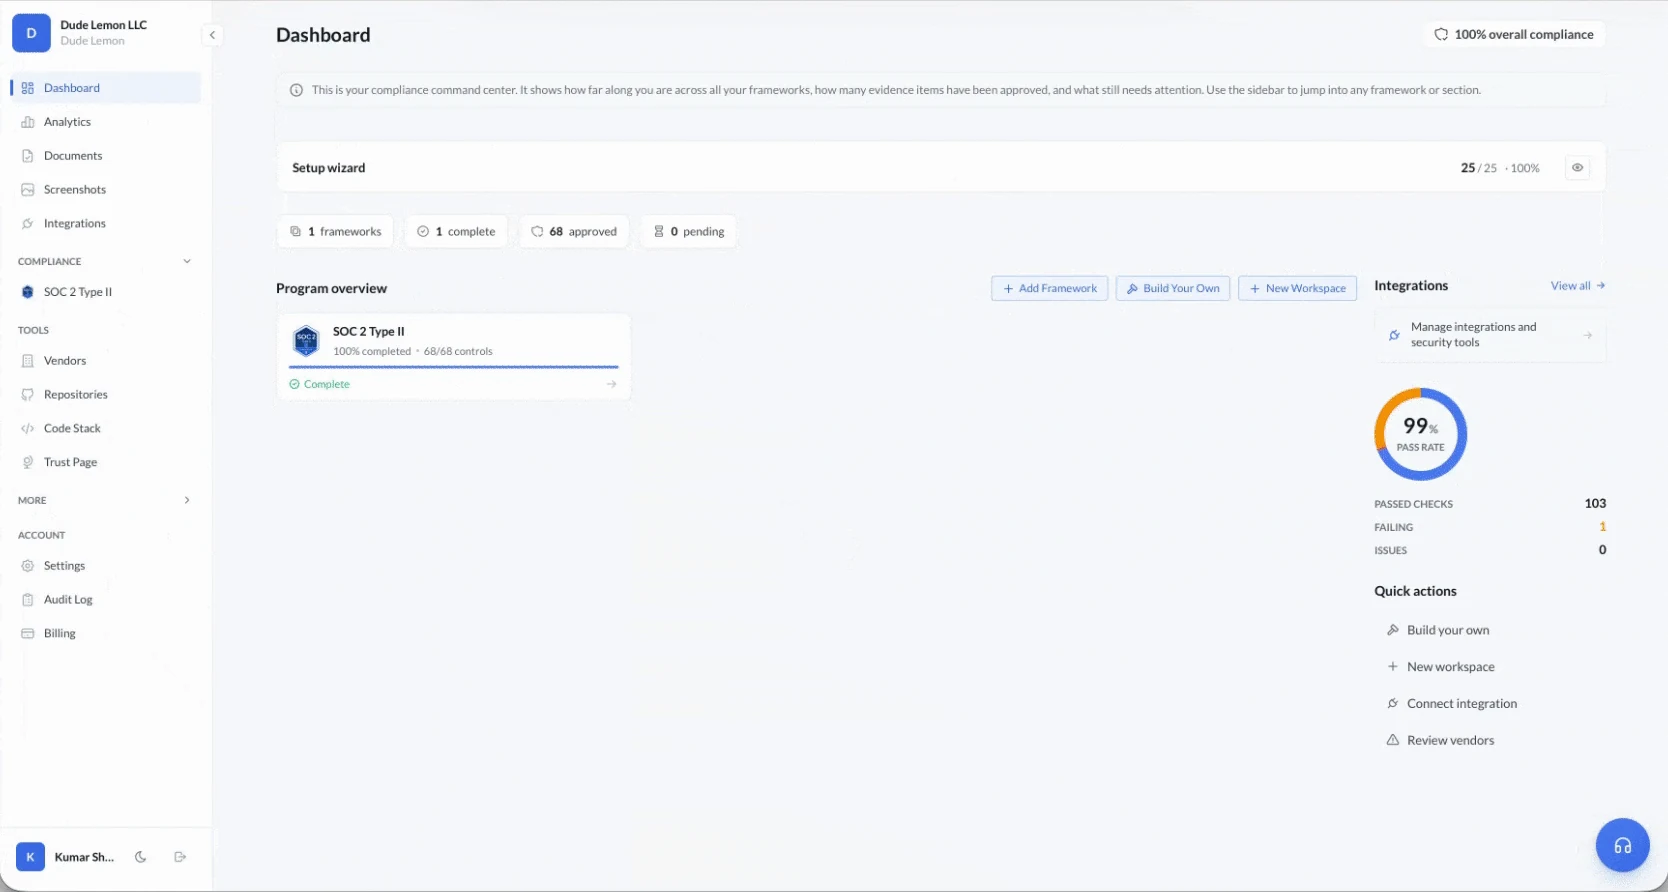
GDPR in the console, control by control.
01GDPR
Seven principles
Article 5, the principles every processing activity is measured against.
- 01
Lawfulness, Fairness & Transparency
Process personal data lawfully with clear communication to data subjects about how their data is used.
- 02
Purpose Limitation
Collect data for specified, explicit, and legitimate purposes. No further processing incompatible with those purposes.
- 03
Data Minimization
Collect only data that is adequate, relevant, and limited to what is necessary for the processing purposes.
- 04
Accuracy
Keep personal data accurate and up to date. Take reasonable steps to erase or rectify inaccurate data.
- 05
Storage Limitation
Retain personal data only for as long as necessary for the purposes it was collected.
- 06
Integrity & Confidentiality
Process data securely using appropriate technical and organizational measures against unauthorized access or loss.
02What Evidr does
Everything GDPR asks for, handled.
- 01
Automated Data Mapping
Discover and document personal data across your systems. AI identifies data flows, processing activities, and third-party transfers for your Records of Processing Activities (RoPA).
- 02
Consent Management
Track consent across all touchpoints. Document lawful basis for each processing activity, manage consent withdrawals, and maintain audit trails of consent history.
- 03
DPIA Automation
Streamlined Data Protection Impact Assessments with guided questionnaires, risk scoring, and mitigation recommendations. Generate audit-ready DPIA documentation.
- 04
Data Subject Rights Portal
Handle access, rectification, erasure, and portability requests. Track response times, manage workflows, and demonstrate compliance with 30-day deadlines.
- 05
Breach Notification Workflows
Document incidents, assess severity, and track 72-hour notification deadlines. Generate DPA notifications and affected individual communications.
- 06
Processor Due Diligence
Assess data processors for GDPR compliance. Manage Data Processing Agreements, track sub-processor changes, and monitor ongoing compliance status.
03The path
GDPR readiness, step by step.
- 01Week 1-2
Data Discovery & Mapping
Identify all personal data processing activities, data flows, and third-party transfers. Build your Records of Processing Activities.
- 02Week 2-3
Legal Basis & Consent Review
Document lawful basis for each processing activity. Review consent mechanisms and update privacy notices as needed.
- 03Week 3-5
Technical & Organizational Measures
Implement appropriate security controls. Establish data retention policies, access controls, and encryption standards.
- 04Week 5-6
Rights & Breach Processes
Set up data subject request workflows and breach notification procedures. Train staff on response protocols.
- 05Week 6-8
Vendor Assessment & DPAs
Review processor relationships, conduct due diligence, and ensure compliant Data Processing Agreements are in place.
04Questions
GDPR, answered.
Related
Often paired with GDPR.
Ready for GDPR?
Start on the free Starter plan, or talk to us and see GDPR set up on your own stack.