
FedRAMP Authorization
Accelerate your path to FedRAMP authorization
Evidr automates NIST 800-53 control mapping, evidence collection, and continuous monitoring for FedRAMP Low, Moderate, and High. Sell to federal agencies faster with AI-powered compliance automation.
- Controls and evidence requirements mapped in advance
- Every upload read and scored by the AI reviewer
- Policies, monitoring and the auditor portal included
Inside the product
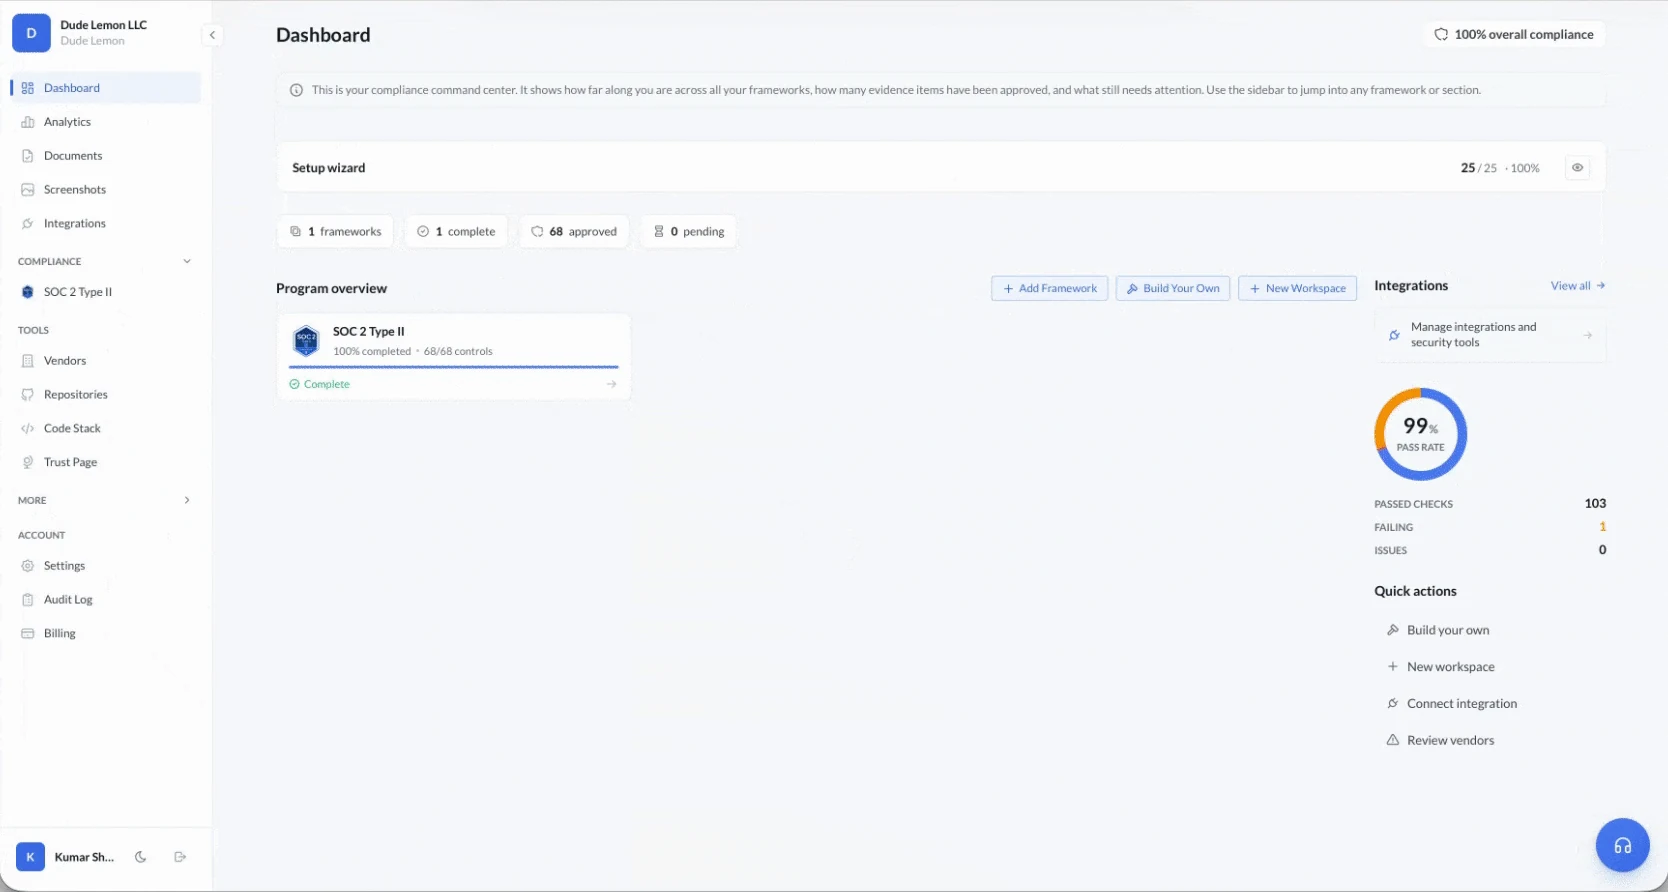
FedRAMP in the console, control by control.
01FedRAMP
Impact levels
Low, Moderate and High, sized by the harm a breach would do.
- 01156
Low
Minimal adverse effect on operations. Suitable for publicly available data.
- 02325
Moderate
Serious adverse effect. Covers 80% of federal cloud use cases.
- 03421
High
Severe or catastrophic effect. Required for classified or sensitive data.
02FedRAMP
NIST 800-53 control families
Every family in the baseline, with the number of controls Evidr maps in each.
- ACAccess Control25
- AUAudit and Accountability16
- ATAwareness and Training5
- CMConfiguration Management11
- CPContingency Planning13
- IAIdentification and Authentication12
- IRIncident Response10
- MAMaintenance6
- MPMedia Protection8
- PEPhysical and Environmental Protection20
- PLPlanning9
- PSPersonnel Security9
- RARisk Assessment7
- CASecurity Assessment and Authorization9
- SCSystem and Communications Protection44
- SISystem and Information Integrity17
- SASystem and Services Acquisition23
- PMProgram Management16
03What Evidr does
Everything FedRAMP asks for, handled.
- 01
NIST 800-53 Control Mapping
Evidr automatically maps your infrastructure to NIST 800-53 controls. See exactly which controls are covered and where gaps exist across all 18 control families.
- 02
System Security Plan Generation
Generate FedRAMP-compliant SSP documentation with AI assistance. Pre-populated templates, control implementation descriptions, and boundary diagrams.
- 03
Continuous Monitoring (ConMon)
Meet FedRAMP ConMon requirements with automated evidence collection, vulnerability tracking, and monthly deliverable generation.
- 04
POA&M Management
Track and manage Plans of Action and Milestones. Automated remediation workflows, milestone tracking, and deviation request management.
- 05
Evidence Artifact Collection
AI-powered evidence review with confidence scoring. Upload once, map to multiple controls. Automatic classification and tagging for audit readiness.
- 06
Agency Collaboration Portal
Secure read-only access for your sponsoring agency and 3PAO assessors. They see approved artifacts without accessing sensitive internal data.
04The path
FedRAMP readiness, step by step.
- 01Week 1-2
Readiness Assessment
AI-guided assessment profiles your cloud environment and identifies gaps against FedRAMP baselines. Generate initial control mapping.
- 02Week 3-8
Documentation Development
Generate SSP, policies, and procedures with AI assistance. Complete control implementation statements and boundary documentation.
- 03Week 8-14
Evidence Collection
Upload evidence artifacts for each control. AI reviews with confidence scoring and maps to NIST control families automatically.
- 04Week 14-16
3PAO Assessment Prep
Internal review of all controls and documentation. Address findings and prepare for third-party assessment organization engagement.
- 05Week 16+
Authorization Package
Submit complete authorization package to your sponsoring agency or JAB. Track review status and address questions.
05Questions
FedRAMP, answered.
Related
Often paired with FedRAMP.
Ready for FedRAMP?
Start on the free Starter plan, or talk to us and see FedRAMP set up on your own stack.