
Compliance Frameworks
One platform, every framework you need
Evidr supports 14 regulatory frameworks including SOC 2, ISO 27001, HIPAA, GDPR, PCI DSS, and FedRAMP. AI-powered automation maps your controls, collects evidence, and tracks readiness across all frameworks simultaneously.
Inside the product
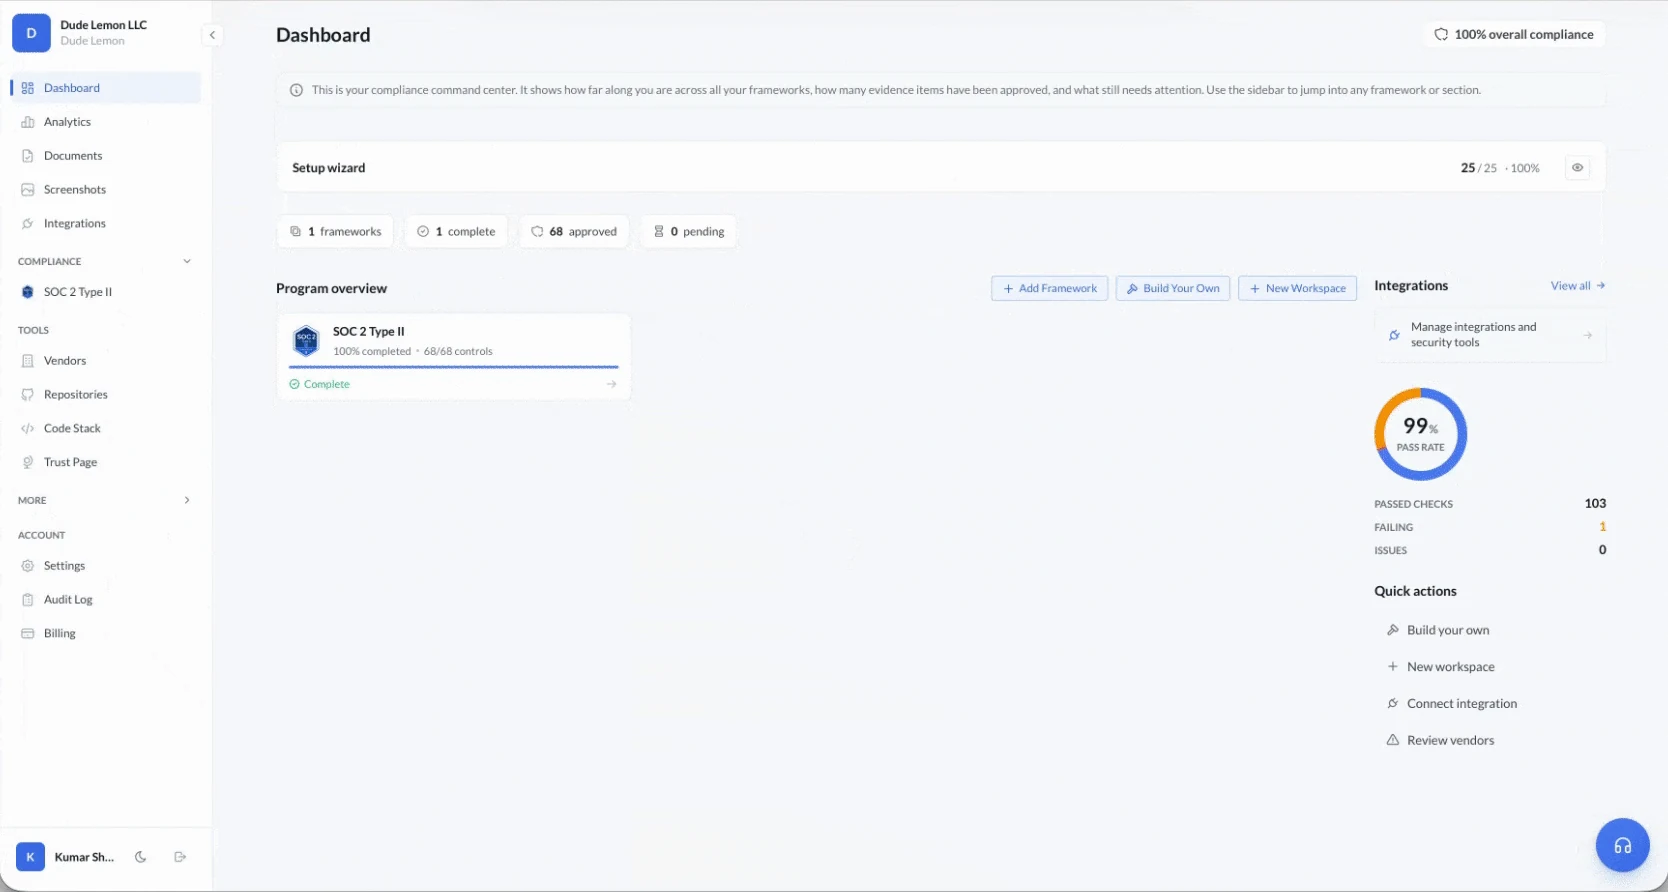
Every framework in one workspace, each with its readiness.
01The catalogue
Fourteen frameworks, all on every plan.
Each comes with pre-mapped controls, evidence requirements and AI gap analysis. Evidence uploaded for one satisfies the overlap in the others.
Security and trust
- 117 controlsSOC 2SOC 2 Type I and Type IIThe gold standard for SaaS security. Demonstrate trust to enterprise customers with audited controls across security, availability, confidentiality, and more.Read the guide
- 93 controlsISO 27001ISO/IEC 27001:2022International standard for information security management systems. Essential for global enterprises and organizations handling sensitive data.Read the guide
- 264 controlsPCI DSSPayment Card Industry Data Security Standard v4.0Required for any organization that stores, processes, or transmits credit card data. 12 core requirements across 6 control objectives.Read the guide
- HITRUSTHITRUST CSFEvidr automates control mapping across 50+ harmonized frameworks, evidence collection, and maturity tracking. Get HITRUST e1, i1, or r2 certified with confidence.Read the guide
Privacy
- 72 controlsGDPRGeneral Data Protection RegulationEuropean Union data protection law governing how organizations collect, process, and store personal data of EU residents.Read the guide
- CCPACalifornia Consumer Privacy Act, as amended by the CPRAEvidr automates CCPA consumer rights management, data inventory mapping, and DSAR fulfillment. Respond to access requests in days instead of weeks and avoid penalties up to $7,500 per violation.Read the guide
- 89 controlsHIPAAHealth Insurance Portability and Accountability ActRequired for any organization handling protected health information (PHI). Covers administrative, physical, and technical safeguards.Read the guide
Government
- 325 controlsFedRAMPFederal Risk and Authorization Management ProgramUS government security framework for cloud service providers. Required for selling to federal agencies.Read the guide
- StateRAMPStateRAMPEvidr automates NIST control mapping, evidence collection, and continuous monitoring for StateRAMP authorization. Sell to state and local governments across 20+ member states with a single security assessment.Read the guide
- CMMCCybersecurity Maturity Model Certification 2.0Evidr automates NIST 800-171 control mapping, SPRS score calculation, and evidence collection for CMMC Level 1, 2, and 3. Protect CUI, maintain DoD contract eligibility, and prepare for C3PAO assessment.Read the guide
- NIST 800-171NIST SP 800-171 Rev. 2Evidr automates control mapping, SPRS score calculation, and System Security Plan generation for defense contractors. Meet DFARS requirements and prepare for CMMC with AI-powered compliance automation.Read the guide
AI governance
- ISO 42001ISO/IEC 42001:2023Evidr automates AI risk assessment, lifecycle management, and compliance monitoring. Build trust with customers and regulators through certified responsible AI practices.Read the guide
- NIST AI RMFNIST AI Risk Management Framework 1.0Evidr automates NIST AI RMF implementation with structured governance, risk mapping, and continuous monitoring. Build trustworthy AI systems with documented controls across the entire AI lifecycle.Read the guide
- EU AI ActRegulation (EU) 2024/1689Evidr automates EU AI Act compliance with risk classification, conformity assessments, and technical documentation management. Prepare for phased deadlines starting February 2025 and avoid penalties up to 7% of global turnover.Read the guide
Custom frameworks for internal standards or regional rules are included on every plan as well.
02Why one platform
Multi-framework compliance, made simple.
- 01
Unified Dashboard
Track compliance across all frameworks from a single view. See real-time readiness scores and evidence coverage at a glance.
- 02
Cross-Framework Mapping
Evidence uploaded for one framework automatically maps to overlapping requirements in others. Upload once, satisfy many.
- 03
Real-Time Scoring
Continuous monitoring of your compliance posture with instant readiness scoring per framework.
- 04
AI-Powered Selection
Answer a few questions about your business and our AI recommends the right frameworks based on your risk profile.
Ready to get audit-ready?
Start on the free Starter plan, or talk to us about SOC 2, ISO 27001, HIPAA or any framework and see the platform on your own stack.