
HIPAA Compliance
Protect patient data and achieve HIPAA compliance in weeks
Evidr automates evidence collection, safeguard tracking, and continuous monitoring for HIPAA Privacy, Security, and Breach Notification Rules. Get audit-ready faster with AI-powered compliance automation.
Inside the product
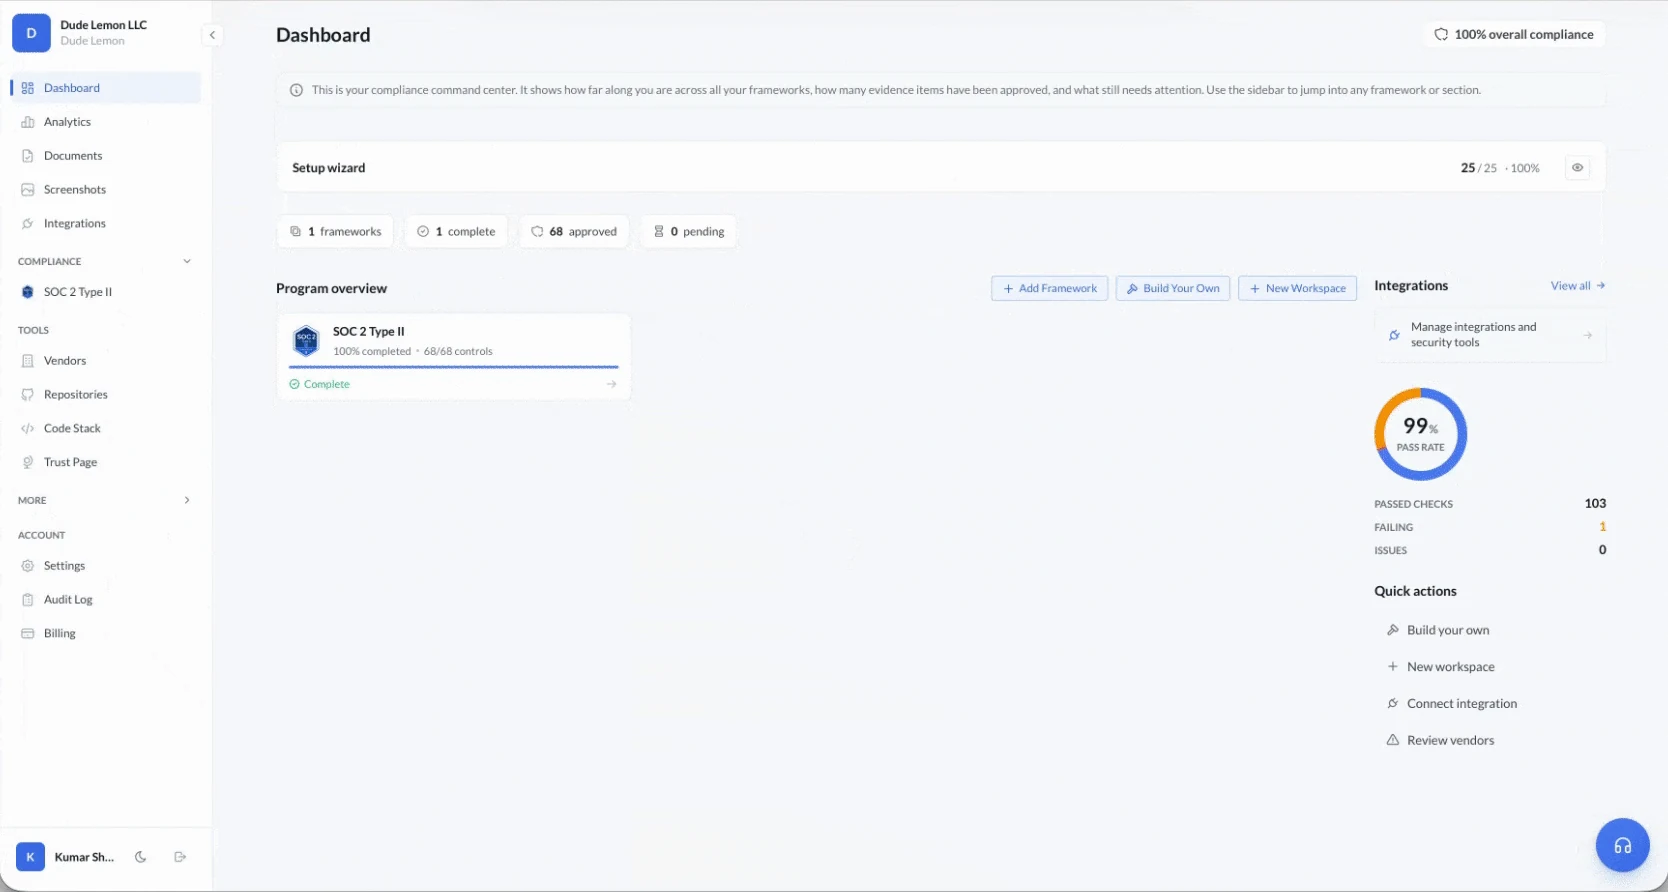
HIPAA in the console, control by control.
01HIPAA
The rules
Privacy, Security, Breach Notification and the safeguards each one asks for.
- 0118 PHI identifiers
Privacy Rule
Standards for protecting individually identifiable health information. Covers permitted uses and disclosures of PHI.
- 0242 specifications
Security Rule
Administrative, physical, and technical safeguards to protect electronic PHI (ePHI).
- 0360-day timeline
Breach Notification Rule
Requirements for notifying affected individuals, HHS, and media following a breach of unsecured PHI.
- 04Up to $1.5M/year
Enforcement Rule
Procedures for investigations, penalties, and hearings for HIPAA violations.
- 05BA liability
Omnibus Rule
Extends HIPAA requirements to Business Associates and strengthens patient rights.
02What Evidr does
Everything HIPAA asks for, handled.
- 01
Privacy Rule Compliance
Track all 18 PHI identifiers and implement required safeguards for patient data protection. Automated mapping to Privacy Rule requirements.
- 02
Security Rule Safeguards
Administrative, physical, and technical safeguard tracking with evidence collection for all HIPAA Security Rule requirements.
- 03
Breach Notification Tracking
Incident response workflows aligned with HIPAA Breach Notification Rule timelines. Document and track breach assessments.
- 04
BAA Management
Track Business Associate Agreements with vendors. Get alerts when BAAs expire or need renewal.
- 05
Workforce Training Tracking
Monitor employee security awareness training completion. Track attestations and annual refresher requirements.
- 06
Risk Assessment
Conduct and document HIPAA-required risk assessments. Track risk mitigation with automated remediation workflows.
03The path
HIPAA readiness, step by step.
- 01Week 1
Risk Assessment
AI-guided risk assessment identifies threats to PHI and evaluates your current safeguards. Required annually by HIPAA.
- 02Week 2
Gap Analysis
Evidr maps your controls to HIPAA requirements and identifies missing safeguards across Privacy, Security, and Breach Notification Rules.
- 03Week 3-4
Policy Implementation
Generate HIPAA-compliant policies and procedures. Access Control, Incident Response, Workforce Training, and more.
- 04Week 4-6
Evidence Collection
Upload evidence for each safeguard. AI reviews documents with confidence scoring and flags missing elements.
- 05Ongoing
Continuous Monitoring
Maintain compliance with automated evidence tracking, BAA expiry alerts, and training completion monitoring.
04Questions
HIPAA, answered.
Related
Often paired with HIPAA.
Ready for HIPAA?
Start on the free Starter plan, or talk to us and see HIPAA set up on your own stack.