
HITRUST CSF Certification
Achieve HITRUST certification faster with AI-powered automation
Evidr automates control mapping across 50+ harmonized frameworks, evidence collection, and maturity tracking. Get HITRUST e1, i1, or r2 certified with confidence.
Inside the product
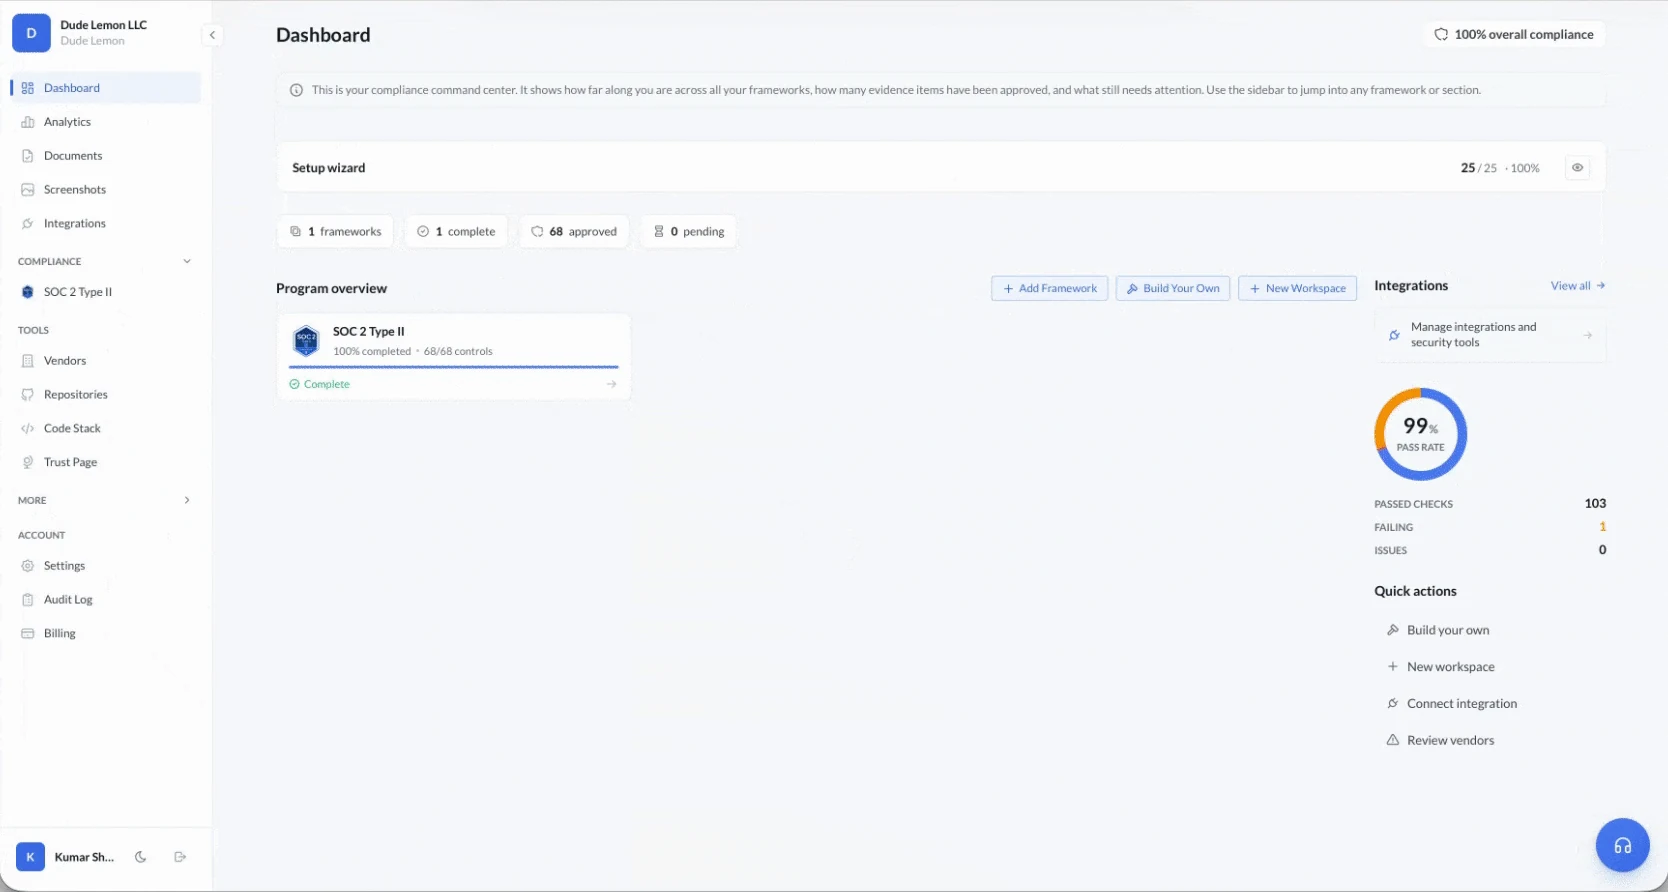
HITRUST in the console, control by control.
01HITRUST
Three assessment types
e1, i1 and r2, from a quick baseline to the full risk-based certification.
- 0144 · 2-4 months
HITRUST e1
Essentials assessment with 44 foundational controls. Demonstrates basic security hygiene.
- 02182 · 4-6 months
HITRUST i1
Implemented assessment with 182 controls. Validates operational security controls are in place.
- 03200+ · 6-12 months
HITRUST r2
Risk-based assessment with 200+ controls based on risk factors. Full HITRUST certification.
02HITRUST
Nineteen control domains
The CSF domains and the controls Evidr maps in each.
- 01Information Protection Program23
- 02Endpoint Protection14
- 03Portable Media Security8
- 04Mobile Device Security11
- 05Wireless Security6
- 06Configuration Management19
- 07Vulnerability Management12
- 08Network Protection18
- 09Transmission Protection14
- 10Password Management9
- 11Access Control24
- 12Audit Logging & Monitoring16
- 13Education & Awareness8
- 14Third Party Assurance15
- 15Incident Management13
- 16Business Continuity17
- 17Risk Management12
- 18Physical & Environmental21
- 19Data Protection & Privacy26
03What Evidr does
Everything HITRUST asks for, handled.
- 01
Harmonized Control Mapping
HITRUST CSF incorporates 50+ authoritative sources including HIPAA, NIST, ISO, and PCI. Evidr maps your controls across all harmonized frameworks simultaneously.
- 02
Maturity Level Tracking
Track implementation maturity across HITRUST's 5-level scale (Policy, Procedure, Implemented, Measured, Managed). Visualize readiness at each maturity level.
- 03
Assessment Type Selection
Choose between e1 (essentials), i1 (implemented), or r2 (risk-based) assessments. Evidr tailors control requirements based on your selected assessment type.
- 04
MyCSF Integration Ready
Export evidence and control responses in HITRUST MyCSF format. Streamline assessor collaboration with audit-ready documentation packages.
- 05
AI-Powered Evidence Review
Upload evidence once and let AI review with confidence scoring. Automatic mapping to HITRUST control requirements and maturity levels.
- 06
Control Inheritance
Leverage cloud provider HITRUST certifications. Map inherited controls from AWS, Azure, and GCP to reduce your assessment scope.
04The path
HITRUST readiness, step by step.
- 01Week 1-2
Scoping & Assessment Selection
Define organizational scope, risk factors, and select assessment type (e1, i1, or r2). AI generates tailored control requirements based on your profile.
- 02Week 2-4
Gap Analysis
Evidr maps existing controls to HITRUST requirements. Identify gaps across 19 control domains and prioritize remediation efforts.
- 03Week 4-12
Control Implementation
Implement missing controls with guided workflows. Generate policies, configure technical controls, and document procedures to required maturity levels.
- 04Week 12-16
Evidence Collection
Collect and upload evidence for each control requirement. AI reviews evidence quality and flags incomplete or missing documentation.
- 05Week 16-24
Validated Assessment
Engage a HITRUST-authorized external assessor. They validate controls through the MyCSF portal with your pre-staged evidence.
05Questions
HITRUST, answered.
Related
Often paired with HITRUST.
Ready for HITRUST?
Start on the free Starter plan, or talk to us and see HITRUST set up on your own stack.