
What happens when evidence goes stale?
Every piece of evidence has an expiry date, and you hear before it lapses. Infrastructure scans on AWS, Azure, Google Cloud and Microsoft 365 run 80+ checks, so the record stays current between audits.
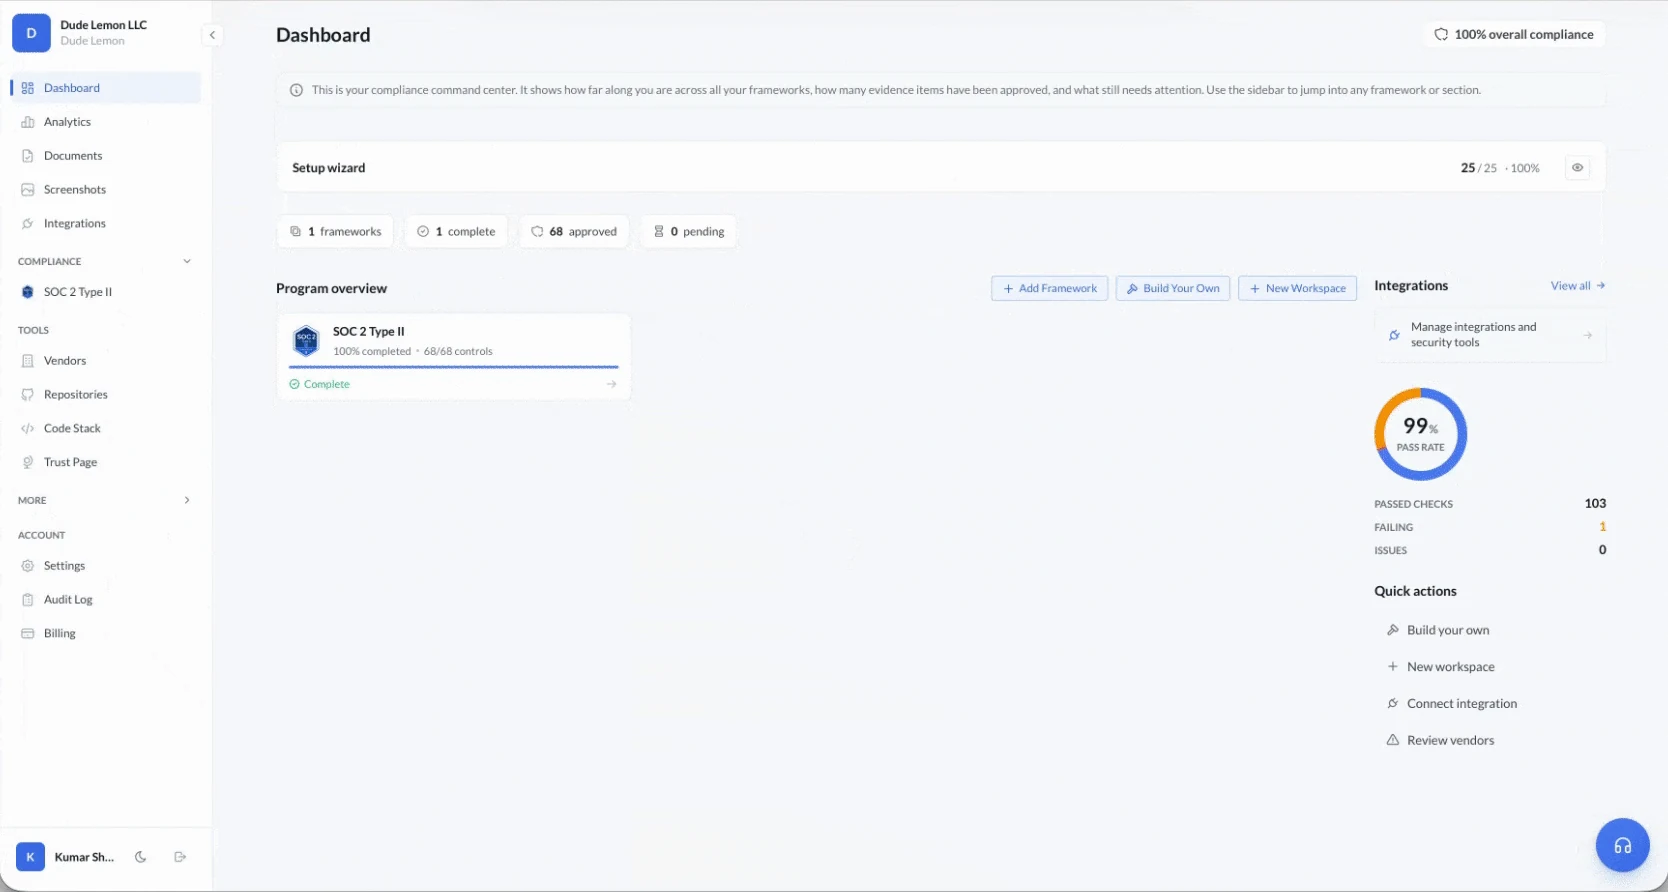
Dude Lemon’s own SOC 2 Type II workspace: readiness, evidence review, policies and vendor alerts.
 Explore the product
Evidence collected from your stack and reviewed by AI. Policies written for you. SOC 2, ISO 27001, HIPAA and eleven more, on every plan.


The problem
Screenshots, exports and spreadsheets go stale before the auditor opens them. Evidr pulls evidence from your stack, reviews every file with AI and keeps it current.
Pull evidence from AWS, Google Cloud, Azure, GitHub and Okta into one audit-ready programme.
Readiness, evidence, policies, monitoring and vendors in one console, with every action anyone takes kept in the audit trail.
Access is granted on least privilege, reviewed every quarter and removed within one business day of a role change.
Every framework you run, scored from the controls and evidence behind it, so you know when to book the audit.
The questions we hear most, each answered by a part of the console.
Every piece of evidence has an expiry date, and you hear before it lapses. Infrastructure scans on AWS, Azure, Google Cloud and Microsoft 365 run 80+ checks, so the record stays current between audits.
No. Every upload gets a confidence score and review notes, and credentials or personal data are caught and held back before anything reaches the auditor.
Evidr drafts them for your company, your stack and your frameworks. You approve each one before it goes live, staff sign it, and the signed PDF is stored as evidence.
All fourteen, on every plan. Each file you add is mapped to the controls it satisfies across frameworks, so one piece of evidence counts for SOC 2, ISO 27001 and HIPAA at once.
A read-only portal with approved evidence and policies, control mappings per framework, version history on every document. Drafts, internal notes, billing and credentials stay hidden, and every action the auditor takes is logged.
From the engineering team
Most teams already do what an auditor asks, and proving it is what takes the weeks, so we built Evidr to collect that proof from your tools as you work.
ShanChief Solutions Architect
Connect on LinkedIn
How onboarding works
A short conversation, and the AI recommends your frameworks.
Controls and policies generated for every framework.
22 read-only connectors pull evidence in on their own.
Controls that do not apply get an auditor-ready reason.
A read-only portal with everything you approved.
Evidr FAQ
Anything we have not answered here, ask us directly at support@evidr.com.
Contact usIt runs a compliance programme end to end: the onboarding AI recommends frameworks and generates controls, integrations pull evidence from your infrastructure, AI reviews every upload with a confidence score, policies are generated and signed, vendors and evidence expiry are monitored, and your auditor gets a read-only portal.
All plans include SOC 2 Type I and II, ISO 27001, ISO 42001, HIPAA, GDPR, PCI DSS, CCPA, HITRUST, FedRAMP, NIST AI RMF, EU AI Act, CMMC, NIST 800-171, StateRAMP and custom frameworks. There are no per-framework charges.
Most companies reach SOC 2 Type I audit readiness in two to four weeks. Onboarding takes minutes, integrations connect in about a minute each, and policies generate in seconds. Type II needs an observation period after that, which Evidr keeps you compliant through.
Plans start at $499 a month billed annually, and every plan includes all fourteen frameworks. AI usage is metered separately as pay-as-you-go, at $0.20 per million input tokens and $0.60 per million output tokens, only in months you use it.
No. Integrations are read-only through official APIs and OAuth, with the minimum scopes needed to collect evidence. Tokens are encrypted and can be revoked from either side at any time.
Yes. Invite the auditor from your workspace and they get a read-only portal scoped to the frameworks you choose: approved evidence, policies and control documentation, nothing in draft. Every action they take is logged.